
Supply Chain & Third Party Risk Management (TPRM)
Centralized control of third-party & supply chain cybersecurity – technically verified, compliant and audit-ready.
One dashboard. Clear actions. No complex software.
Technical Verification & Compliance
Concrete Solutions and Clear Assessments
Developed in Austria · from €1,990 per year
For companies to verify their suppliers, subcontractors or subsidiaries.
Companies from all industries trust us

No more incomprehensible security reports and vague requirements
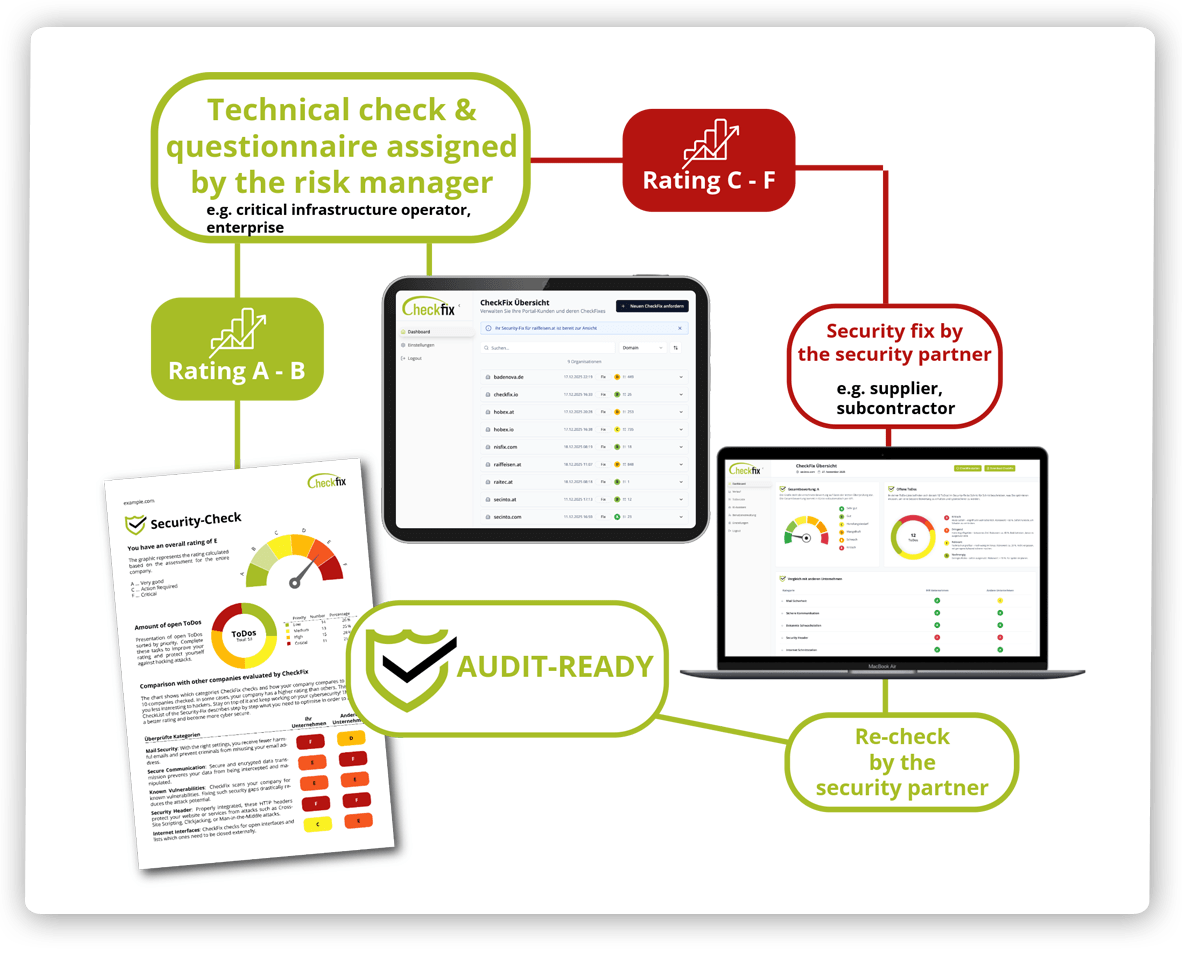
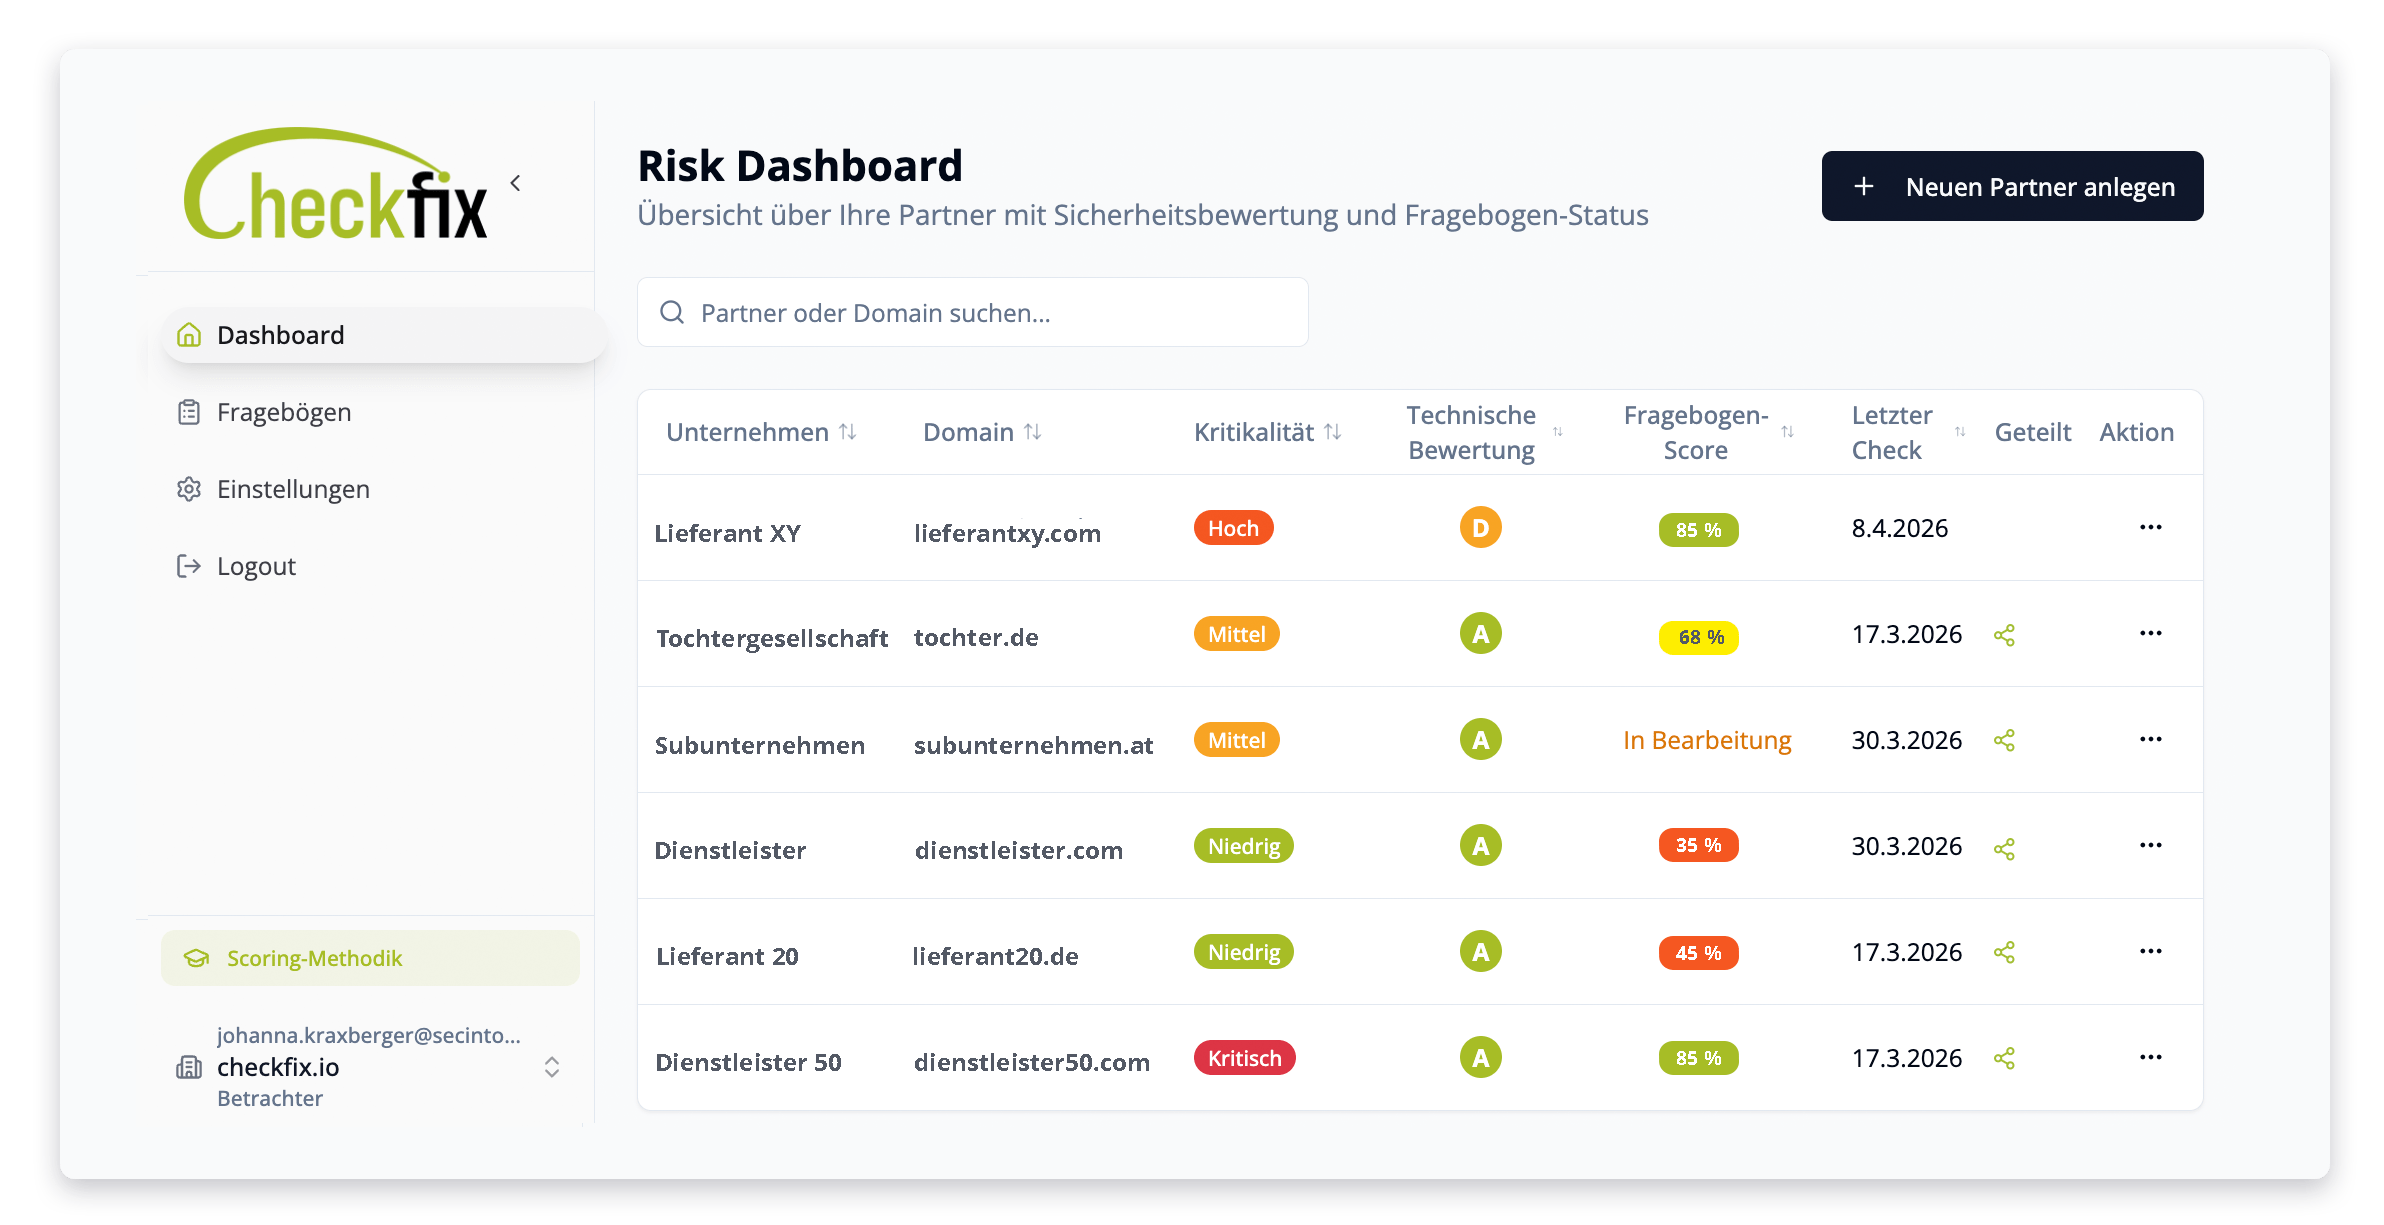
CheckFix shows you as Risk Manager at a glance where your security partners are falling short.
For KRITIS, ISO 27001-obliged companies and corporations with suppliers or subsidiaries.
For KRITIS, ISO 27001-obliged companies and corporations with suppliers or subsidiaries.
🟢 Green?
All good. Audit-ready.
🟡 Yellow?
Room for improvement. To-do list shows what needs to be done.
🔴 Red?
Critical. Concrete fix instructions included.

For Security Partners:
For Security Partners: Technical security analysis and compliance assessment – in one tool. CheckFix shows you exactly where technical gaps exist and which compliance requirements are still missing. To-do list and questionnaires directly in the dashboard – fill in, submit, done. Your green status applies to all clients: prove it once, show it everywhere.
For Security Partners: Technical security analysis and compliance assessment – in one tool. CheckFix shows you exactly where technical gaps exist and which compliance requirements are still missing. To-do list and questionnaires directly in the dashboard – fill in, submit, done. Your green status applies to all clients: prove it once, show it everywhere.
For Risk Managers:
One glance at the dashboard is enough. You immediately see which security partners are secure, where action is needed and where audit risks threaten. CheckFix ensures your partners don’t just get evaluated – they receive clear technical and compliance action items, with every step documented.
One glance at the dashboard is enough. You immediately see which security partners are secure, where action is needed and where audit risks threaten. CheckFix ensures your partners don’t just get evaluated – they receive clear technical and compliance action items, with every step documented.
How to manage third-party risks – centrally from one dashboard
2. Send invitation with one click
CheckFix automatically sends a professional invitation with access link to your security partners.
3. Automated security review + compliance questionnaires
|
Technical (Security Check):
|
Organizational (digital questionnaires):
|
4. Everything at a glance in the dashboard
Technical score: A-F rating of each supplier
Compliance status: 🟢🟡🔴 traffic light system
Critical findings: Which gaps need to be closed?
Audit status: Which supplier is audit-ready?
5. Audit-ready documentation
Audit-ready reports with before/after comparison for BSI evidence and internal audits.
Want to see exactly how CheckFix works?
Understand our intuitive and effective system in just 2 minutes.
Start Interactive Demo
Why CheckFix is a cost-effective solution for NIS-2, supply chain security and other use cases
Only CheckFix offers a solution that combines both technical verification (external security assessment) and organizational compliance measures in one tool.
Measurable cybersecurity for your supply chain
CheckFix makes IT security risks visible and quantifiable – for you and all your service providers through external risk assessments from a hacker's perspective.
For Risk Managers
- Immediately visible: Which service provider has security gaps? Which subsidiary needs to take organizational measures?
- Questionnaires: Templates already comply with guidelines (e.g. NIS2, ISO) or can optionally be created yourself.
- Audit-ready: Before/after documentation for authorities
- Benchmarking: Objective comparison of all security partners
For Security Partners
- Easy proof to all clients and other risk managers – whether external or within a corporation
- Concrete guidance: What exactly needs to be fixed? Where do organizational measures need to be taken?
- Competitive advantage: Green score = trustworthy partner = higher contract chances
What CheckFix technically checks
CheckFix analyzes the external attack surface from a hacker's perspective – fully automated in 15 steps. No agents, no access to internal systems.
The 5 most important test areas
Email Security
SPF, DKIM, DMARC configuration → Prevents phishing and email spoofing
Encryption (TLS/SSL)
TLS versions, cipher strength, certificates → Protects data during transmission
Known Vulnerabilities (CVEs)
Software versions vs. vulnerability databases → Protects against ransomware
Web Security (Security Headers)
CSP, HSTS, X-Frame-Options → Prevents XSS and clickjacking
Exposed Services
Open ports and accessible services → Minimizes attack surface
Here you can find details on the 10 additional test steps: DNS configuration, blacklist status, cookie security, subdomain scanning, SSL/TLS best practices and more.
Transparent annual prices – no hidden costs
CheckFix Risk Manager STARTER
€1,990/year
Recommended for most KRITIS operators
- Manage up to 25 service providers in the portal
- Automated invitation system for your
service providers - Technical risk assessment via external
security analysis - Compliance assessment based on
ISO 27001, NIS-2, BSI or your own requirements - Central dashboard: Third party risks at a glance
- Audit-ready reports for NIS-2, ISO 27001 & DORA
- Email support
CheckFix Risk Manager PREMIUM
€3,990/year
For larger organizations
- Manage up to 100 service providers in the portal
- Automated invitation system for your
service providers - Technical risk assessment via external
security analysis - Compliance assessment based on
ISO 27001, NIS-2, BSI or your own requirements - Central dashboard: Third party risks at a glance
- Audit-ready reports for NIS-2, ISO 27001 & DORA
- Semi-annual security review call
- Priority email & phone support
CheckFix Risk Manager CUSTOM
On request
For complex infrastructures or specific requirements
- Individual number of service providers
- Flexible credits for regular security checks
- Provide CheckFix for your suppliers
including tasks & fix strategy - Dedicated account manager
- API access
- Custom reports & integrations
For security partners (suppliers, service providers, subcontractors): Were you invited by your client? → See CheckFix Premium (€950/year)
Why KRITIS operators use CheckFix
Fully Automated
Zero-touch assessment in 24 hours
- Technical infrastructure analysis without manual intervention
- No agent deployment, no firewall adjustments
- Compliance questionnaires are automatically sent
Technical AND Compliance in 1 Tool
External security check + organizational measures
- Automated vulnerability analysis (A-F score) + compliance questionnaires (BSI, ISO 27001)
- Traffic light system for organizational measures (🟢🟡🔴)
Central TPRM Overview
Technical score + compliance status in one dashboard
- Manage up to 100 service providers
- A-F score + compliance traffic light (🟢🟡🔴) at a glance
- Automatic invitations with all requirements
Concrete Action Instructions
Prioritized to-do lists instead of endless reports
- Technical: Fix instructions by priority (Critical → Low)
- Organizational: Template documents for missing evidence (ISMS, incident response) – available on request
- What needs to be done? Where exactly? How urgent?
Before/After Documentation
Audit-ready evidence for technical AND organizational improvements
- Initial check → Fix → Re-check with score improvement
- Compliance gaps → Measures → Traffic light status 🟢
- Complete documentation for audits
Made in Austria
German-speaking support & GDPR compliant
- No US cloud, no vendor lock-in
- Personal support from Austria
- Hosting in the EU – perfect for KRITIS
Frequently Asked Questions
How exactly does a check cycle work?
A check cycle consists of two components:
Technical review:
- Initial assessment: Complete external analysis of IT infrastructure (max. 24 hours)
- Re-check: After remediation of vulnerabilities, we check again and document the improvement
Organizational review (optional):
- Compliance questionnaires according to BSI, ISO 27001 or DIN SPEC 27076
- Traffic light rating in percent – fully customizable
The result: Audit-ready before/after documentation for technical AND organizational security measures.
What does “external analysis” mean?
CheckFix only scans what an attacker from the internet would also see:
- Your public IP addresses
- Accessible domains and subdomains
- Open ports and services
- TLS configurations
- DNS records
We do not penetrate your systems. No internal scans, no agents, no admin rights required.
Which compliance questionnaires does CheckFix offer?
CheckFix provides pre-made questionnaires based on established standards:
- BSI IT-Grundschutz: IT baseline protection requirements for critical infrastructures
- ISO 27001: Internationally recognized standard for information security management systems
- DIN SPEC 27076: Requirements for information security in the supply chain
You can use the pre-made templates or create your own questionnaires.
Are 2 check cycles per year sufficient for NIS2?
Yes. NIS2 requires “regular risk assessments” but does not define a minimum frequency.
Two structured check cycles per year with documented improvements are best practice for medium-sized KRITIS operators and meet NIS2 requirements for both technical and organizational risk assessments.
Daily monitoring (like SecurityScorecard) is not required for NIS2.
Does CheckFix replace my GRC software?
CheckFix is the technical AND organizational complement to your internal compliance processes.
- GRC tools manage: Internal policies, workflows, document management, internal audits
- CheckFix delivers: External technical security data, vulnerability analysis, measurable scores AND compliance assessments of your service providers, subcontractors, etc.
CheckFix focuses on auditing your supply chain – technically and organizationally. For your own internal processes, you continue to use your GRC software.
Is CheckFix NIS2 compliant?
CheckFix comprehensively meets NIS2 requirements for external risk assessments:
Technical:
- Regular external assessments -2 cycles/year (depending on the model, suppliers purchase CheckFix Premium separately or checks are already included in the Risk Manager)
- Vulnerability identification and remediation
- Before/after documentation
Organizational:
- Compliance questionnaires according to recognized standards
- Evidence of security measures (ISMS, incident response, etc.)
- Supply chain risk management
- Audit-ready documentation
CheckFix covers both pillars of NIS2 requirements for your supply chain: technical security AND organizational measures.
How does the invitation of security partners work?
The process is fully automated:
- You perform an initial check of the service provider domain (results after max. 24 hours)
- You see the technical result in the portal (A-F score)
- Optional: You add compliance questionnaires (BSI, ISO 27001, own templates)
- Click “Invite security partner”
- Automatic email with: Link to check result + access to questionnaires + to-do list + template documents
- Security partner fixes vulnerabilities and completes questionnaires
- You see updated result in portal: Technical score + compliance traffic light (🟢🟡🔴)
Can service providers use their score for multiple clients?
Yes – as long as they have an active CheckFix subscription. Both the technical CheckFix score and the compliance evidence are independent external assessments.
A service provider with green status (technical A-B + organizational 🟢) can use these proofs for any number of KRITIS clients – without having to fill out new questionnaires or perform security assessments each time.
This saves time and costs on both sides.
What happens if a service provider does not meet compliance requirements?
CheckFix makes the process transparent and actionable:
- Live preview: While filling in the questionnaire, the service provider instantly sees how each answer affects the rating – before submitting.
- Weighting visible: The point distribution shows which requirements matter most – and where improvements have the biggest impact.
- Concrete gaps: The questions themselves reveal exactly which measures are missing or incomplete.
- Submit & approval: Once satisfied with the result, the service provider submits the questionnaire. The risk manager reviews it, can add comments, accept – or return it with a note.
This way, a red status becomes step by step a green one – measurably and audit-ready documented.
Ready to become a CheckFix Risk Manager?
Book a personal demo and see how CheckFix automates your third-party risk management.
- ✅ 30-minute live demo of the portal
- ✅ Free test check for your domain
- ✅ Setup in 24 hours
- ✅ No credit card required