Third Party Risk Management (TPRM)
Prove the IT security of your supply chain – every service provider technically verified & organizationally assessed.
One dashboard. Clear actions. First results within 24 h.
Technical Verification & Compliance
Concrete Solutions and Clear Assessments
Developed in Austria · from €1,990 per year
For companies verifying their suppliers, subcontractors or subsidiaries.
Companies from all industries trust us

Third Party Risk Management (TPRM)
Prove the IT security of your supply chain – every service provider technically verified & organizationally assessed.
One dashboard. Clear actions. First results within 24 h.
Technical Verification & Compliance
Concrete Solutions and Clear Assessments
Developed in Austria · from €1,990 per year
For companies verifying their suppliers, subcontractors or subsidiaries.
Companies from all industries trust us
No more incomprehensible security reports and vague requirements
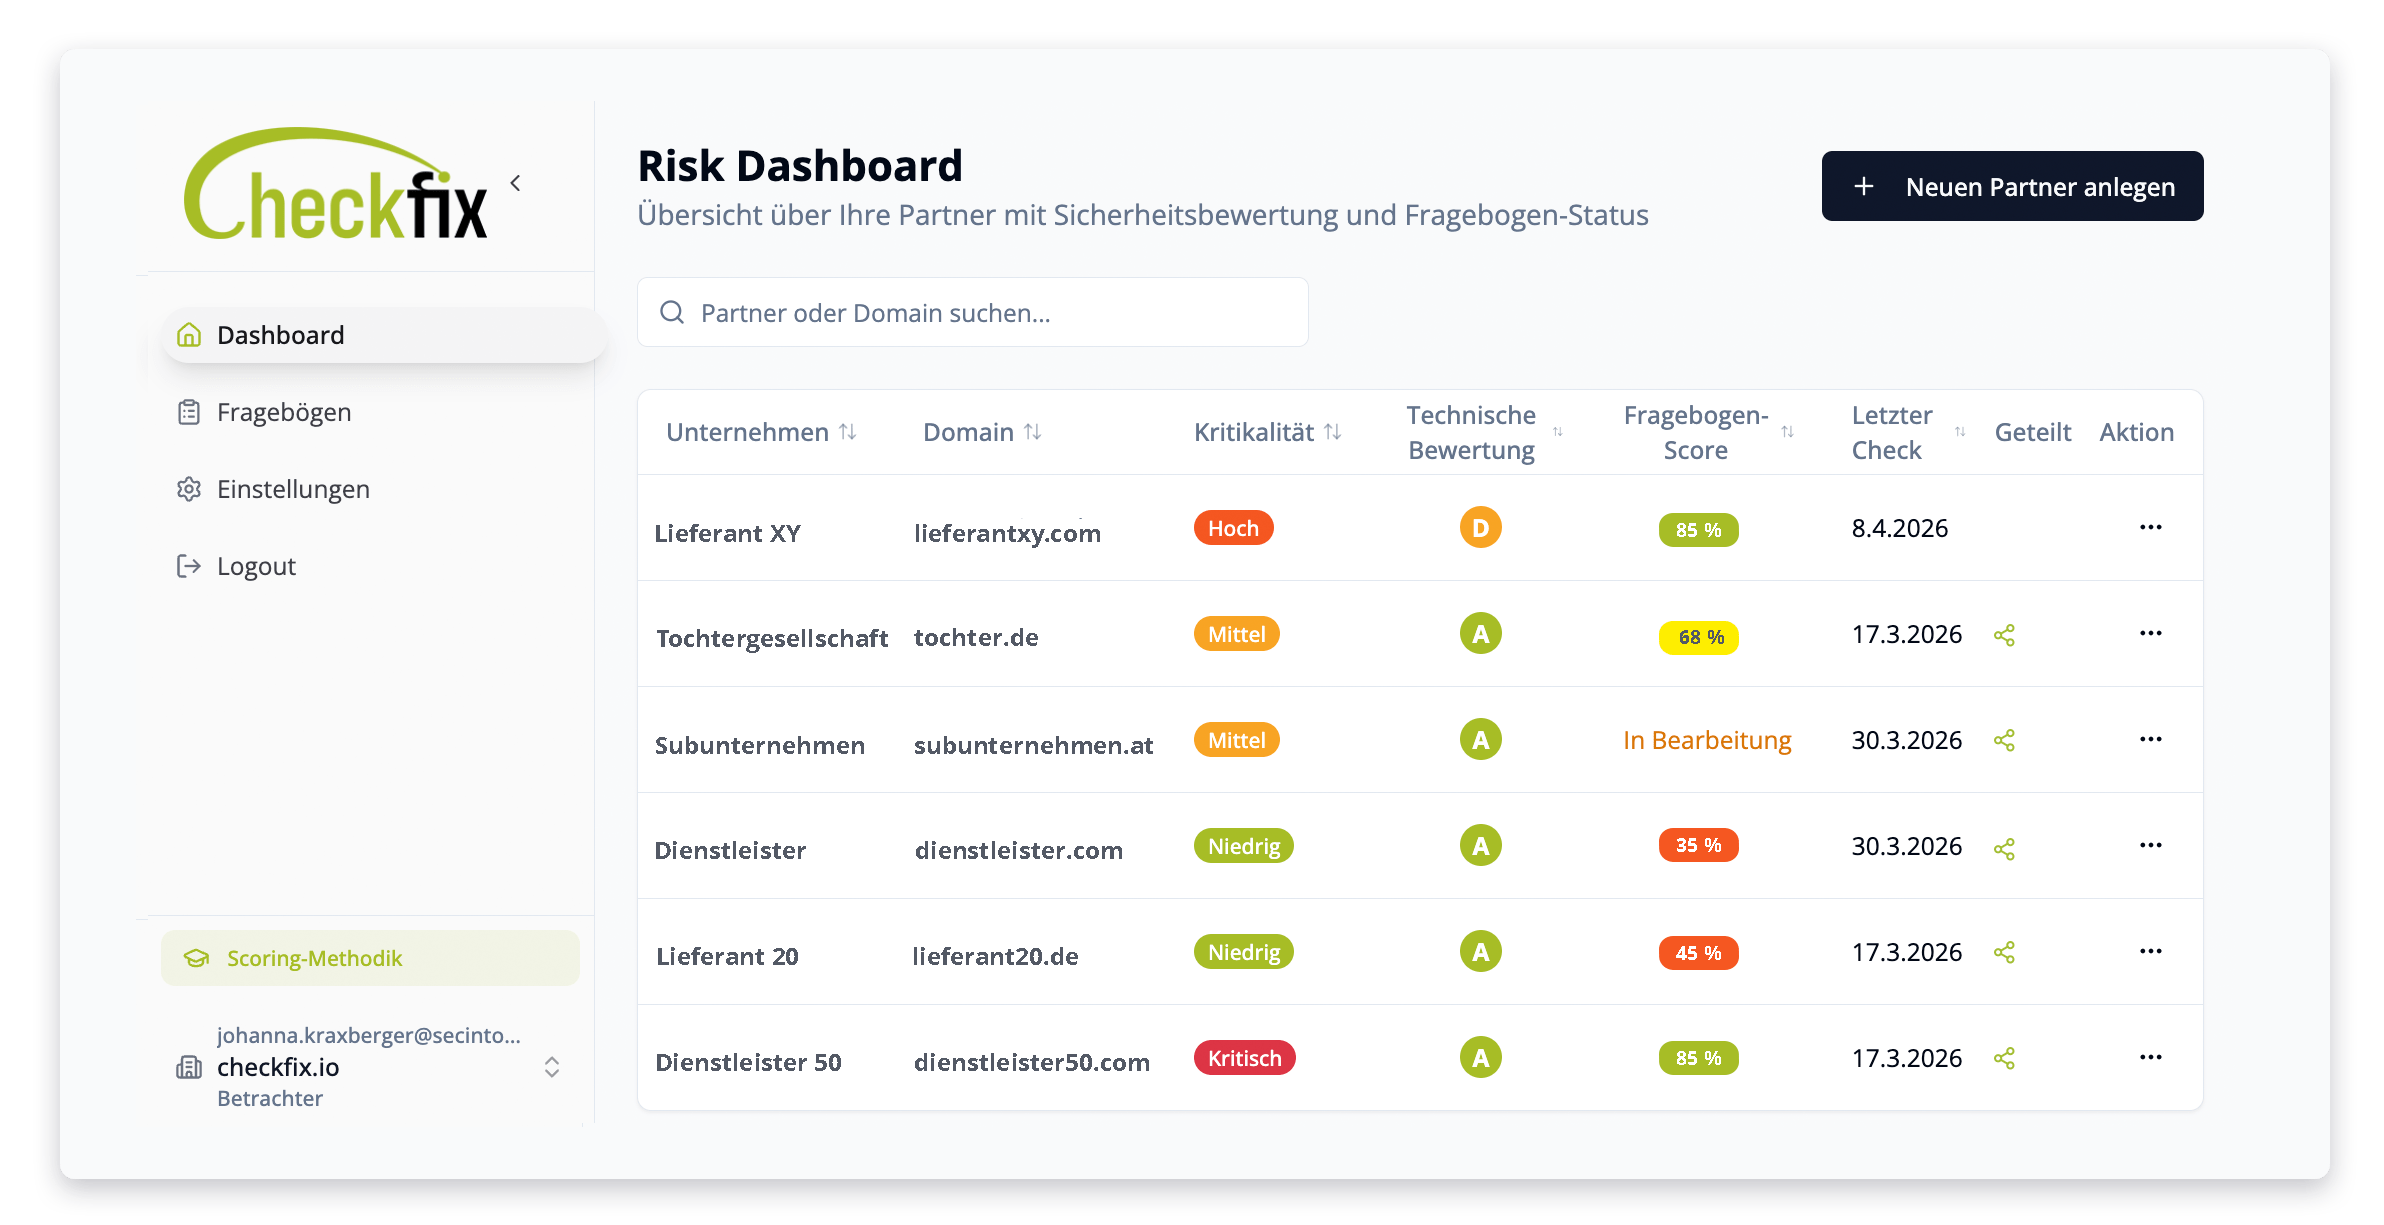
CheckFix shows you as a risk manager at a glance where your security partners are falling short.
For KRITIS operators, ISO 27001-obligated companies and corporate groups with suppliers or subsidiaries.
For KRITIS operators, ISO 27001-obligated companies and corporate groups with suppliers or subsidiaries.
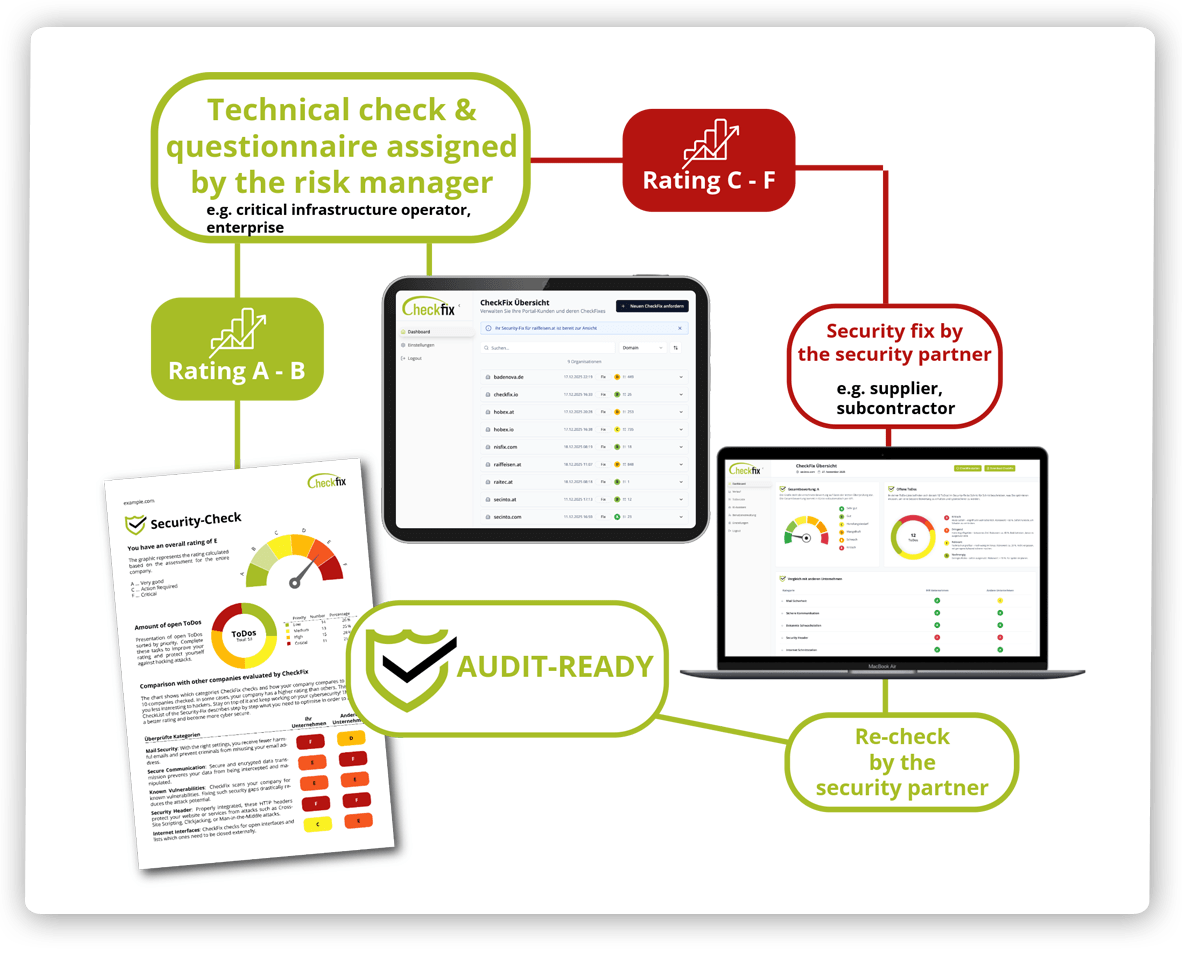
Green?
All good. Audit-ready.
Yellow?
Room for improvement. The to-do list shows what needs to be done.
Red?
Critical. Concrete fix strategy included.
For security partners:
Technical security analysis and compliance assessment – in one tool. CheckFix shows you exactly where technical gaps exist and which compliance requirements are still missing. To-do list and questionnaires directly in the dashboard – fill in, submit, done. Your green status applies to all clients: prove it once, show it everywhere.
Technical security analysis and compliance assessment – in one tool. CheckFix shows you exactly where technical gaps exist and which compliance requirements are still missing. To-do list and questionnaires directly in the dashboard – fill in, submit, done. Your green status applies to all clients: prove it once, show it everywhere.
For risk managers:
One glance at the dashboard is enough. You immediately see which security partners are secure, where action is needed and where audit risks loom. CheckFix ensures that your partners are not only assessed but also receive clear technical measures – including traceable implementation.
One glance at the dashboard is enough. You immediately see which security partners are secure, where action is needed and where audit risks loom. CheckFix ensures that your partners are not only assessed but also receive clear technical measures – including traceable implementation.
What is the CheckFix Risk Manager?
The CheckFix Risk Manager is software for Third Party Risk Management (TPRM), tailored to the European market and regulations such as NIS2. Companies use it to check the IT security of their suppliers, service providers, third-party vendors and subsidiaries: technically with an external security assessment from an attacker’s perspective, organizationally with digital questionnaires. They document the result with an A–F rating and an audit-ready report.
How to manage third party risks – centrally from one dashboard
1. Add security partners in the dashboard
Add your suppliers, service providers, subsidiaries or subcontractors.
2. Send invitations with one click
CheckFix automatically sends a professional invitation with an access link to your security partners.
3. Automated security check + compliance questionnaires
|
Technical (Security Check):
|
Organizational (digital questionnaires):
|
4. Everything at a glance in the dashboard
Technical score: A-F rating of each supplier
Compliance status: traffic light system
Critical findings: Which gaps need to be closed?
Audit status: Which supplier is audit-ready?
5. Audit-ready documentation
Audit-ready documentation of your supply chain’s IT security in a clear dashboard. Including progress.
Want to know exactly how CheckFix works?
Understand our clear and effective system in just 2 minutes.
Start interactive demo
Why CheckFix is a cost-effective solution for NIS2, TISAX, supply chain security and other use cases
Only CheckFix offers a solution that combines technical verification (external security assessment) and organizational compliance measures in one tool.
| Requirement | CheckFix Solution |
|---|---|
| Supply Chain Security |
Central management of all business units/suppliers in one central security dashboard – status at a glance |
| Risk Management | A-F score per security partner – TECHNICAL & ORGANIZATIONAL |
| Documentation Requirements | Audit-ready reports with before/after comparison |
| Regular Review | 2 check cycles per year – sufficient for NIS2 and most companies |
| Incident Prevention | Prioritized to-do lists for vulnerability remediation |
| TISAX® (automotive) | Assess suppliers technically and via questionnaire – results as an audit-ready report for your TISAX® documentation |
Measurable cybersecurity for your supply chain
CheckFix makes IT security risks visible and quantifiable – for you and all your service providers, through external risk assessments from a hacker's perspective.
For risk managers
- Immediately visible: Which service provider has security gaps? Which subsidiary needs to take compliance measures?
- Questionnaires: Templates already comply with guidelines (e.g. NIS2, ISO 27001) or can be created yourself.
- Audit-ready: Before/after documentation for authorities
- Benchmarking: Objective comparison of all security partners
For security partners
- Easy proof to all clients and other risk managers – whether external or within a corporate group
- Concrete guidance: What exactly needs to be fixed? Where do organizational measures need to be taken?
- Competitive advantage: Green score = trustworthy partner = better chances of winning contracts
What CheckFix checks technically
CheckFix analyzes the external attack surface from a hacker's perspective – fully automated in 15 steps. No agents, no access to internal systems.
The 5 most important test areas
Email Security
SPF, DKIM, DMARC configuration → Prevents phishing and email spoofing
Encryption (TLS/SSL)
TLS versions, cipher strength, certificates → Protects data in transit
Known Vulnerabilities (CVEs)
Software versions vs. vulnerability databases → Protects against ransomware
Web Security (Security Headers)
CSP, HSTS, X-Frame-Options → Prevents XSS and clickjacking
Exposed Services
Open ports and accessible services → Minimizes the attack surface
Find details on the 10 additional test steps here: DNS configuration, blacklist status, cookie security, subdomain scanning, SSL/TLS best practices and more.
One system, two ways
PartnerCheck – check and assess
You assess your partners technically and organizationally. Each partner sees their A–F rating and the Security Check report. If needed, the partner books the complete to-do list and action plan themselves (CheckFix Basic or Premium).
PartnerFix – check, assess and send the to-dos along
Your partners receive the technical to-dos right away. You cover the cost of CheckFix and require that the security gaps found are fixed.
Right for you if you want to actively manage and prove the security of your supply chain.
Included in both versions
External security assessment from an attacker’s perspective (A–F rating), digital compliance questionnaires with scoring, central dashboard for overview and progress, and audit-ready documentation.
Transparent annual prices – no hidden costs
One system, two ways. Every plan is available as PartnerCheck (check and assess) or PartnerFix (check, assess and to-do list for remediation). The technical check, questionnaires with scoring and the dashboard are included in both – the only difference is who pays for the full CheckFix for remediation: With PartnerCheck, your partner books the to-dos themselves if needed; with PartnerFix, you take care of it and stay in control.
STARTER
25 credits · up to 25 partners
PartnerCheck: €1,990/year
PartnerFix: €3,990/year
Recommended for most KRITIS operators
PROFESSIONAL
100 credits · up to 100 partners
PartnerCheck: €3,990/year
PartnerFix: €9,990/year
Recommended for mid-sized companies with a larger partner list
BUSINESS & MORE
more than 100 partners
PartnerCheck & PartnerFix: on request
More partners? Talk to us – we’ll put together your package.
Included in both versions
- External security assessment per partner (A–F rating)
- Digital compliance questionnaires (ISO 27001, NIS2, BSI or your own)
- Central dashboard: third party risks at a glance
- Automated invitation system for your partners
- 1 credit per check or re-check. Every re-check is a full CheckFix with a new rating and up-to-date results.
- Unused credits remain available; questionnaires can be used without limits
Should any technical issues arise with the dashboard, we are of course on hand right away. If you need expert support, it can be booked at €150 / hour.
For security partners (suppliers, service providers, subcontractors): Invited by your client? → See CheckFix Premium (€950/year)
Why KRITIS operators use CheckFix
Fully automated
Zero-touch assessment in 24 hours
- Technical infrastructure analysis without manual intervention
- No agent deployment, no firewall adjustments
- Compliance questionnaires are sent automatically
Technical AND compliance in 1 tool
External security check + organizational measures
- External security assessment (A-F score) + compliance questionnaires (BSI, ISO 27001)
- Traffic light system (in percent) for compliance measures ()
Central TPRM overview
Technical score + compliance status in one dashboard
- Manage up to 100 service providers
- A-F technical score + compliance assessment at a glance
- Automatic invitations with all requirements
Concrete action instructions
Prioritized to-do lists instead of endless reports
- Technical: Fix strategy by priority (Critical → Low)
- Organizational: Questionnaires show exactly which evidence is missing
- What needs to be done? Where exactly? How urgent?
Before/after documentation
Audit-ready evidence for technical AND organizational improvements
- Initial check → Fix → Re-check with score improvement
- Compliance gaps → visible from the scoring system
- Complete documentation for audits
Made in Austria
Support in German and English & GDPR-compliant
- No US cloud
- Personal support from Austria
- Hosting in the EU – perfect for KRITIS
Frequently Asked Questions
How do I check the IT security of my suppliers?
With an external security assessment per supplier: CheckFix checks from an attacker’s perspective what is reachable from the outside – mail configuration, TLS/SSL, known vulnerabilities (CVEs), security headers and open services. This results in an A-F rating with a prioritized to-do list for each supplier. The check starts without any involvement from the supplier.
You additionally assess the organizational side with digital questionnaires (BSI, ISO 27001, DIN SPEC 27076 or your own). This gives you the technical status quo and compliance status in one dashboard.
Is a questionnaire or self-assessment sufficient as proof?
A questionnaire shows the supplier’s self-assessment. The external security assessment shows the actual technical status quo: it checks from the internet what is really reachable and secured – regardless of the information in the questionnaire.
Both together – technical findings and digital questionnaire – provide reliable, audit-ready proof.
Which suppliers do I have to assess under NIS2?
NIS2 requires you to manage security in the relationship with your direct suppliers and service providers – that is, the suppliers and service providers you work with directly. In doing so, you take into account the specific vulnerabilities and the cybersecurity practices of each of them.
Particular focus: providers with access to your systems or data and those that are critical to your operations. A service provider does not have to fall under NIS2 itself – what matters is your direct business relationship.
In CheckFix, you add these security partners, prioritize them by criticality and check them technically and organizationally.
What does NIS2 require for supply chain security?
NIS2 requires affected companies to actively manage the security of their supply chain: assess the IT security of their suppliers and service providers, document risks and follow up on measures. Technical risk assessments and organizational evidence are required.
CheckFix covers both – external security assessment per supplier plus compliance questionnaires – and documents the result in an audit-ready way.
How exactly does a check cycle work?
A check cycle consists of two components:
Technical review:
- Initial assessment: Complete external analysis of the IT infrastructure (max. 24 hours)
- Re-check: After the vulnerabilities have been fixed, we check again and document the improvement
Organizational review (optional):
- Compliance questionnaires based on BSI, ISO 27001 or DIN SPEC 27076
- Traffic light rating in percent can be fully customized
The result: Audit-ready before/after documentation for technical AND organizational security measures.
What does “external analysis” mean?
CheckFix only scans what an attacker could also see from the internet:
- Your public IP addresses
- Reachable domains and subdomains
- Open ports and services
- TLS configurations
- DNS records
We do not penetrate your systems. No internal scans, no agents, no admin rights required.
Which compliance questionnaires does CheckFix offer?
CheckFix provides ready-made questionnaires based on established standards:
- BSI IT-Grundschutz: IT baseline protection requirements for critical infrastructures
- ISO 27001: Internationally recognized standard for information security management systems
- DIN SPEC 27076: Requirements for information security in the supply chain
You can use the ready-made templates or create your own questionnaires.
Are 2 check cycles per year sufficient for NIS2?
Yes. NIS2 requires “regular risk assessments” but does not define a minimum frequency.
Two structured check cycles per year with documented improvements are best practice for mid-sized KRITIS operators and meet the NIS2 requirement for both technical and organizational risk assessments.
Daily monitoring (as with SecurityScorecard) is not required for NIS2.
Is CheckFix NIS2-compliant?
CheckFix comprehensively meets the NIS2 requirements for external risk assessments:
Technical:
- Regular external assessments – 2 cycles/year (depending on the model, the supplier purchases CheckFix Premium for this, or the checks are already included in the Risk Manager)
- Vulnerability identification and remediation
- Before/after documentation
Organizational:
- Compliance questionnaires based on recognized standards
- Evidence of security measures (ISMS, incident response, etc.)
- Supply chain risk management
- Audit-ready documentation
CheckFix covers both pillars of the NIS2 requirements for your supply chain: technical security AND organizational measures.
NIS2, DORA and ISO 27001 – what is the difference in the supply chain?
ISO 27001 is a voluntary standard for an information security management system. NIS2 is a legal obligation for many companies and explicitly requires supply chain security to be managed. DORA applies specifically to the financial sector and sets similar requirements for third-party service providers.
What they all have in common: you must assess and prove the IT security of your suppliers. CheckFix provides the technical and organizational basis for this – regardless of which framework applies to you.
Does the Risk Manager help with TISAX®?
Yes. You assess your service providers technically with an external security assessment and organizationally with digital questionnaires based on ISO 27001 or your own requirements. You use the audit-ready report for your TISAX® documentation.
Does CheckFix replace my GRC software?
CheckFix is the technical AND organizational complement to your internal compliance processes.
- GRC tools manage: Internal policies, workflows, document management, internal audits
- CheckFix delivers: External technical security data, vulnerability analysis, measurable scores AND compliance assessments of your service providers, subcontractors and the like.
CheckFix focuses on checking your supply chain – technically and organizationally. For your own internal processes, you continue to use your GRC software.
How does inviting security partners work?
The process is fully automated:
- You run an initial check of the service provider’s domain (results within max. 24 hours)
- You see the technical result in the portal (A-F score)
- Optional: You add compliance questionnaires (BSI, ISO 27001, your own templates)
- Click on “Invite security partner”
- Automatic email with: link to the check result + access to questionnaires + to-do list + template documents
- The security partner fixes vulnerabilities and completes the questionnaires
- You see the updated result in the portal: technical score + compliance traffic light (green/yellow/red)
Can service providers use their score for multiple clients?
Yes – provided they have a CheckFix subscription. Both the technical CheckFix score and the compliance evidence are independent external assessments.
A service provider with green status (technical A-B + organizational green) can use this evidence for any number of KRITIS clients – without having to fill in new questionnaires or run security assessments each time.
This saves time and costs on both sides.
What happens if a service provider does not meet compliance requirements?
CheckFix makes the process transparent and actionable:
- Live preview: While filling in the questionnaire, the service provider immediately sees how each answer affects the rating – even before submitting.
- Visible weighting: The point distribution shows which requirements are particularly relevant – and where improvements have the greatest impact.
- Concrete gaps: The service provider can see directly from the questions which measures are missing or incomplete.
- Submission & approval: Once the service provider is satisfied with the result, they submit the questionnaire. The risk manager reviews it and can comment, accept – or reject it with a remark.
Step by step, a red status becomes a green one – measurably and documented in an audit-ready way.
What does a supplier assessment with CheckFix cost?
CheckFix Risk Manager is available in two versions: PartnerCheck (check and assess) and PartnerFix (check, assess and have issues fixed).
- PartnerCheck: from €1,990 per year (Starter, up to 25 partners), €3,990 (Professional, up to 100 partners)
- PartnerFix: from €3,990 per year (Starter), €9,990 (Professional, up to 100 partners)
- More than 100 partners: on request
Included in both versions: technical security assessment, compliance questionnaires, central dashboard and audit-ready reports. All prices net, plus VAT.
Ready to become a CheckFix Risk Manager?
Book a personal call and see how CheckFix automates your Third Party Risk Management.
- ✓30-minute live demo of the portal
- ✓Free test check for your domain
- ✓Setup in 24 hours
- ✓Free and non-binding