Security Check with a system:
Find vulnerabilities – fix them – prove it
External attack surface analysis for SMEs, NIS2 and ISO 27001.
No technical jargon. With your technician. Before you get hacked.
Automated external security assessment
Delivers actionable to-dos:
YOUR technician can handle them
Re-check: risk assessment for clients & audits
Technical reports: suitable for NIS2 and ISO 27001
Companies from all industries trust us

How external attack surface analysis works with CheckFix
In just 2 minutes, you’ll understand our simple yet effective approach.
Start Interactive Demo
Cybersecurity with a system – simple, measurable, effective
Find and fix security gaps – developed in Austria
What is CheckFix? The Cybersecurity Check for SMEs
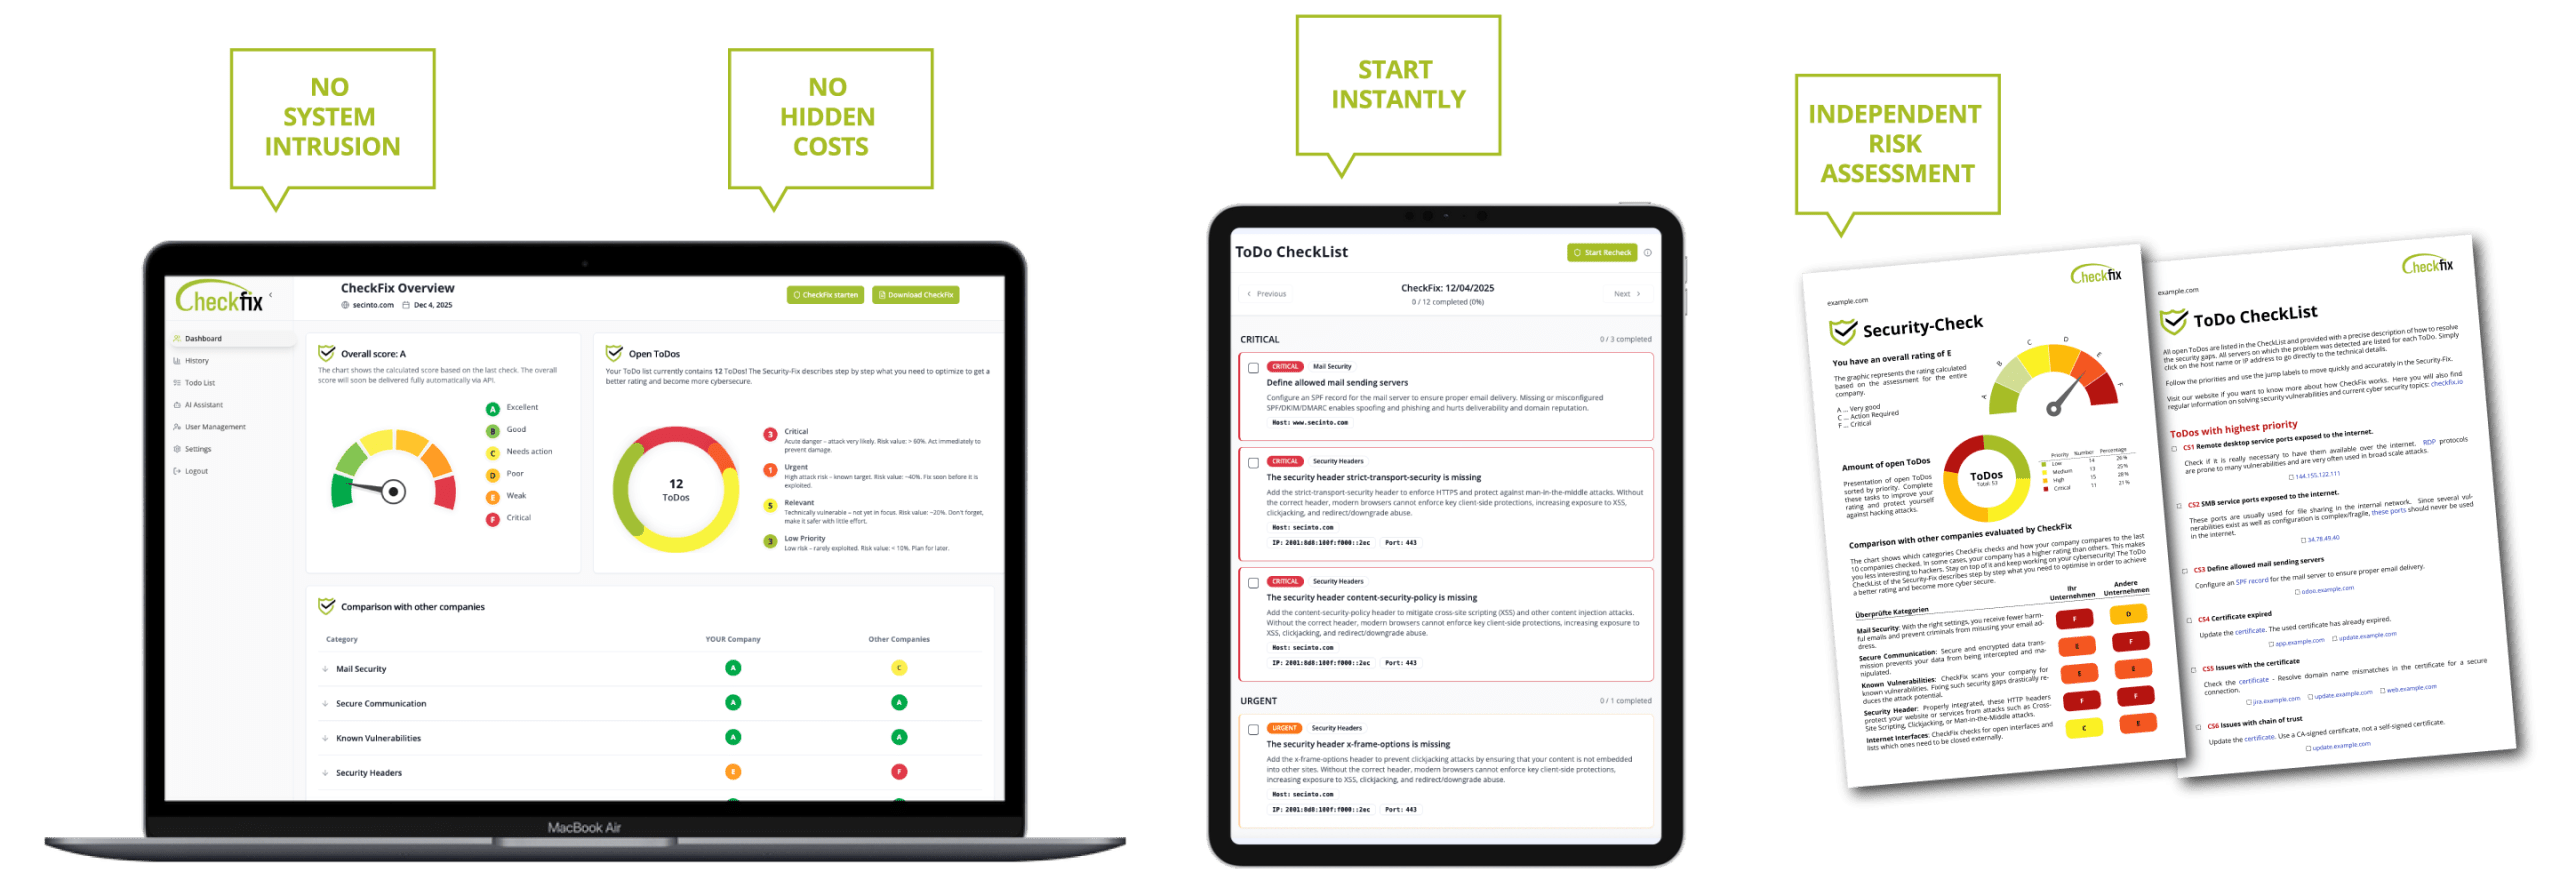
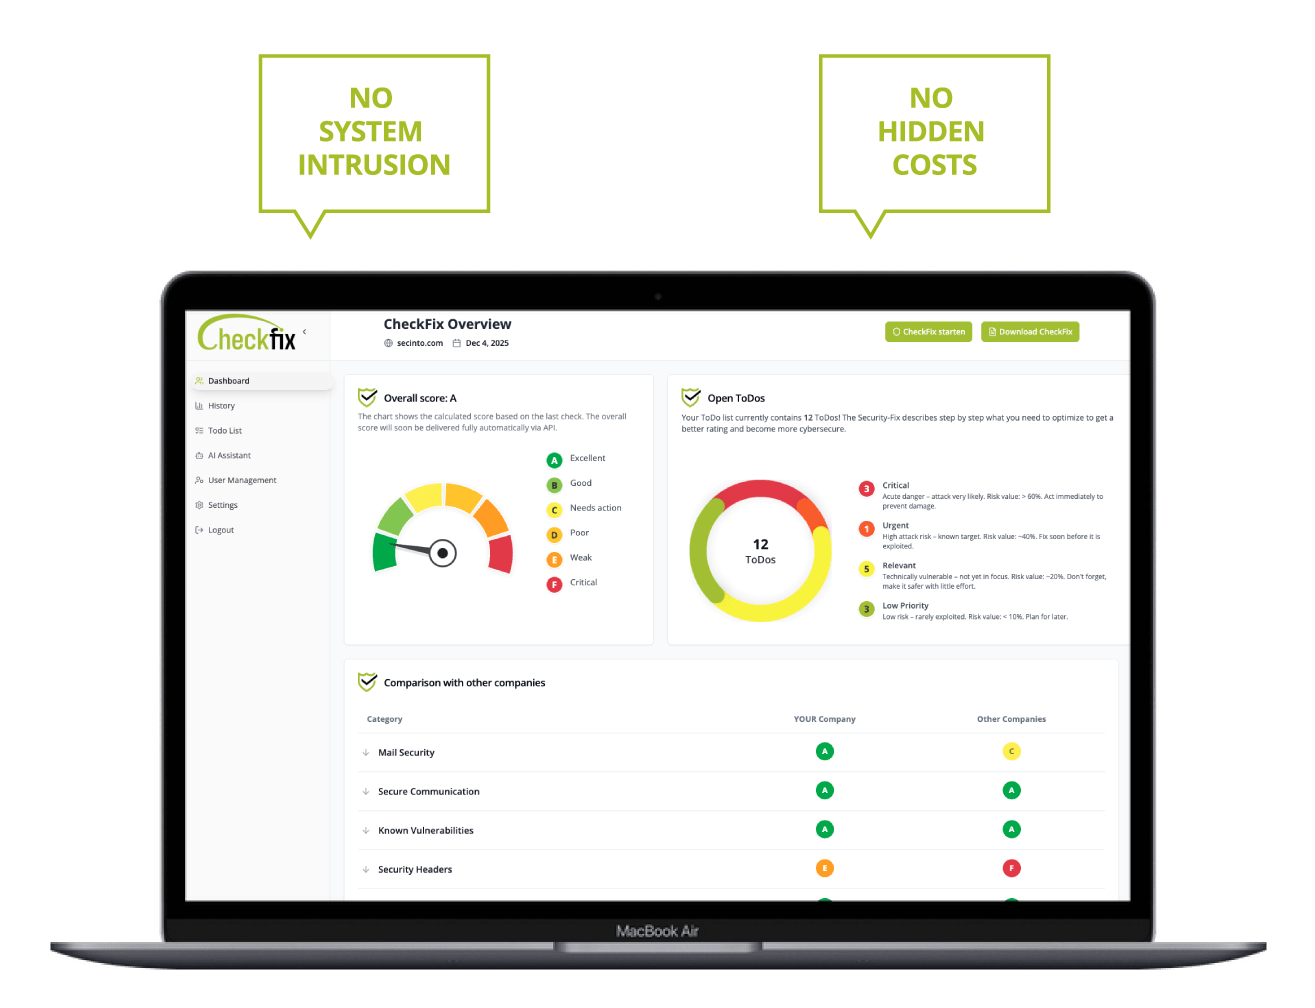
CheckFix is Attack Surface Management from Austria: the automated external attack surface analysis by secinto GmbH. Based on your domain(s), CheckFix performs a complete external security assessment and checks your IT infrastructure from a hacker’s perspective. Your data stays in Europe.
Within 24 hours you receive a prioritized to-do list with a concrete fix strategy that your own technician can implement.
Anything that can’t be fixed right away is documented directly in the to-do list: reason, compensating measure, deadline and owner. CheckFix turns this into a PDF report with an action plan and management response. Use it for your own audit, for example under NIS2, NISG 2026, ISO 27001, DORA or TISAX®, or send it to any customer who asks for proof of IT security.
If you want to go deeper, you can add the AI Pentest on top of CheckFix: our own pentest agent on our own hardware shows how the gaps found could be exploited. Our pentesters monitor the system continuously and keep developing it.
✓ Automated · ✓ In 24h · ✓ No frills · ✓ Made in Austria
What CheckFix checks
Attack Surface Management across 5 check areas
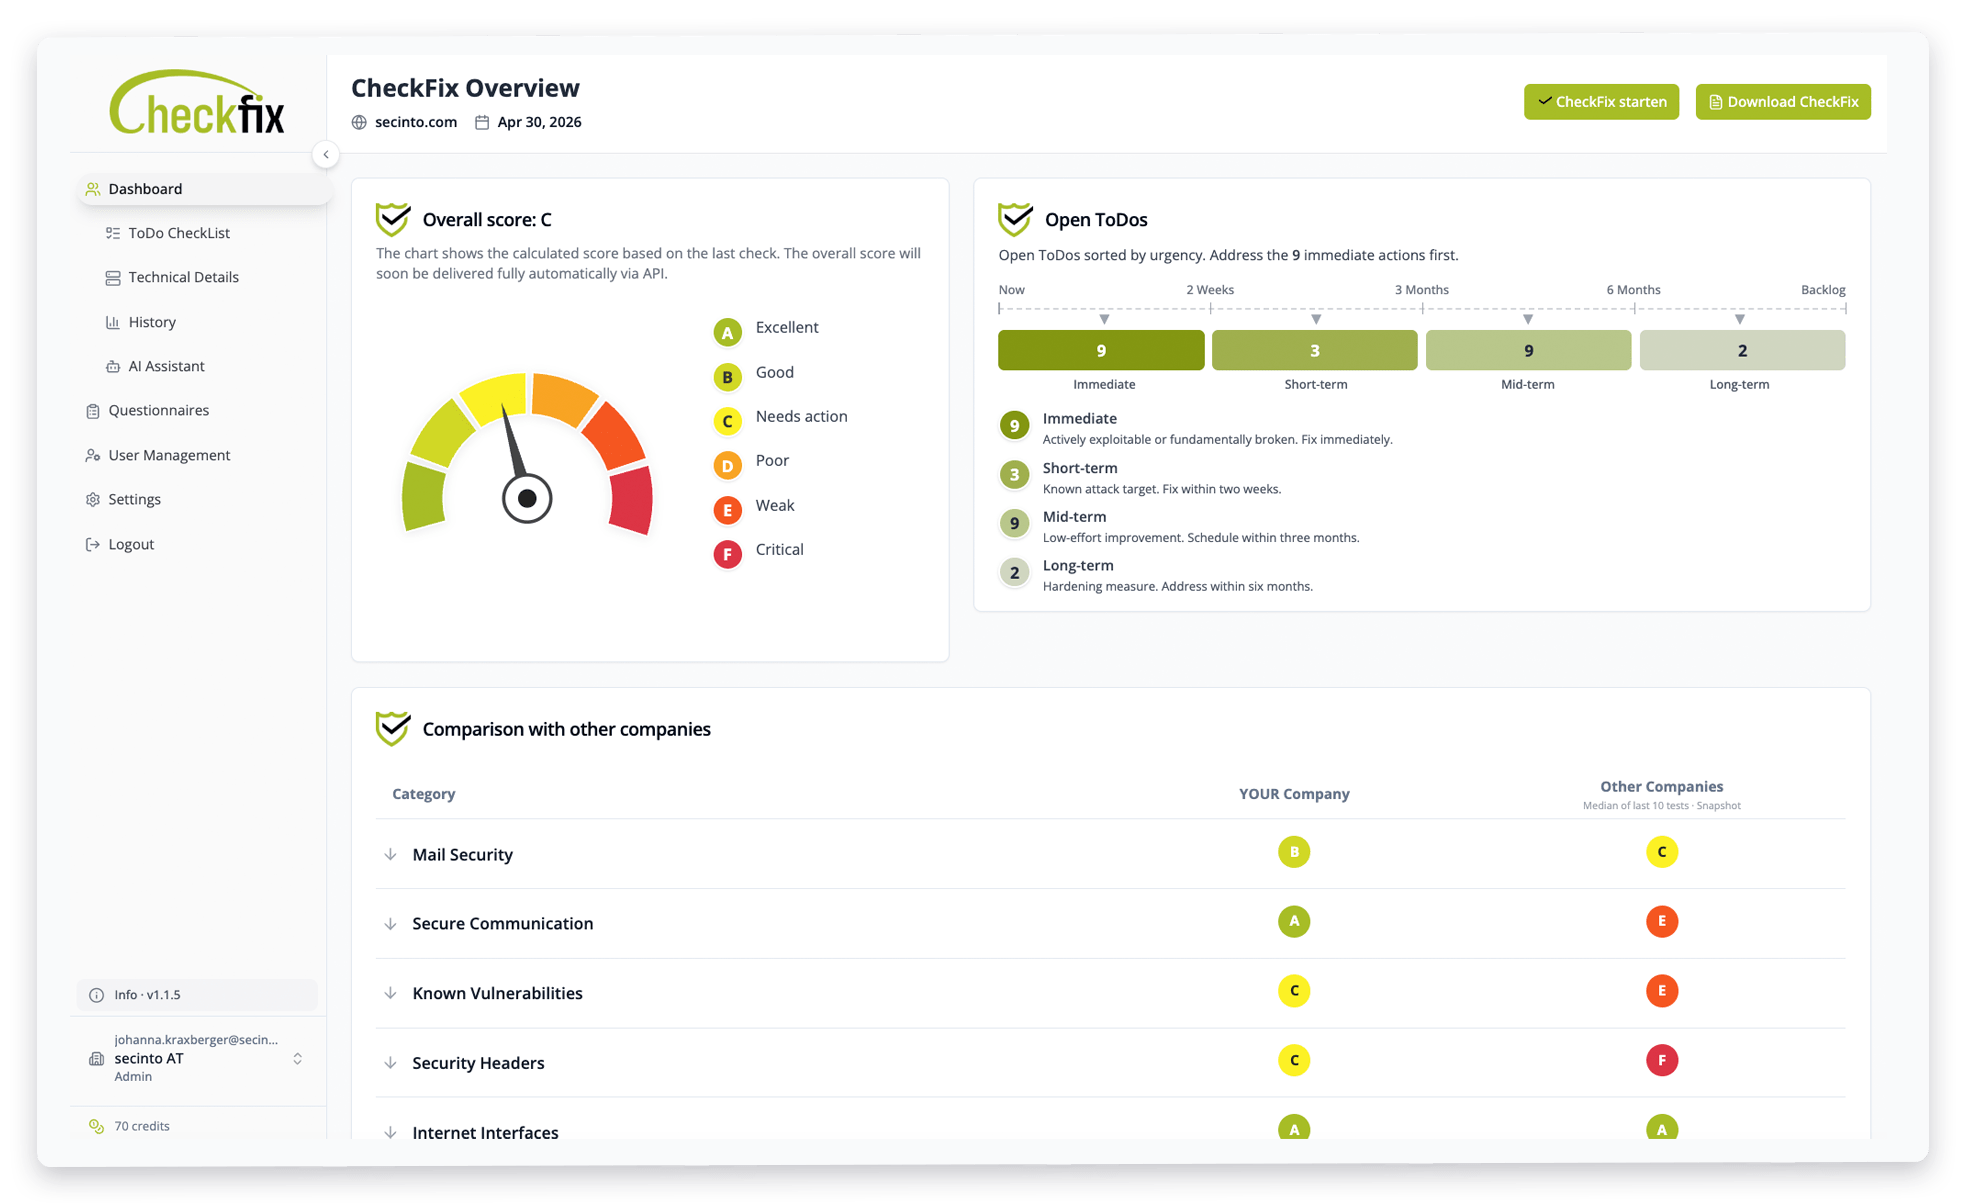
Mail security
In many of our checks, the mail settings are configured incorrectly – and a stranger can send e-mails in your name. Fake invoices to your customers, for example.
Secure communication (TLS/SSL)
Outdated encryption or expired certificates: data between your customers and your server can be intercepted, and browsers warn visitors about your website.
Test individual servers right away: free SSL check with Gossling →
Known vulnerabilities (CVEs)
Outdated software has publicly known vulnerabilities. Attackers search for them automatically – often the entry point for ransomware.
Vulnerability management from the outside: with every check, CheckFix compares your reachable services against known CVEs.
Security headers
If certain protective settings are missing on your website, attackers can inject malicious code or intercept your visitors’ input.
Internet interfaces
Forgotten test servers, open databases, remote maintenance access: anything reachable from the internet can be found by attackers too.
How CheckFix works technically: Technical architecture →
What CheckFix does differently
For us, analyzing your cybersecurity is just the beginning – CheckFix takes you from security gap to solution: automated, clear, documented.
External attack surface analysis automated from a hacker’s perspective, without penetrating your system
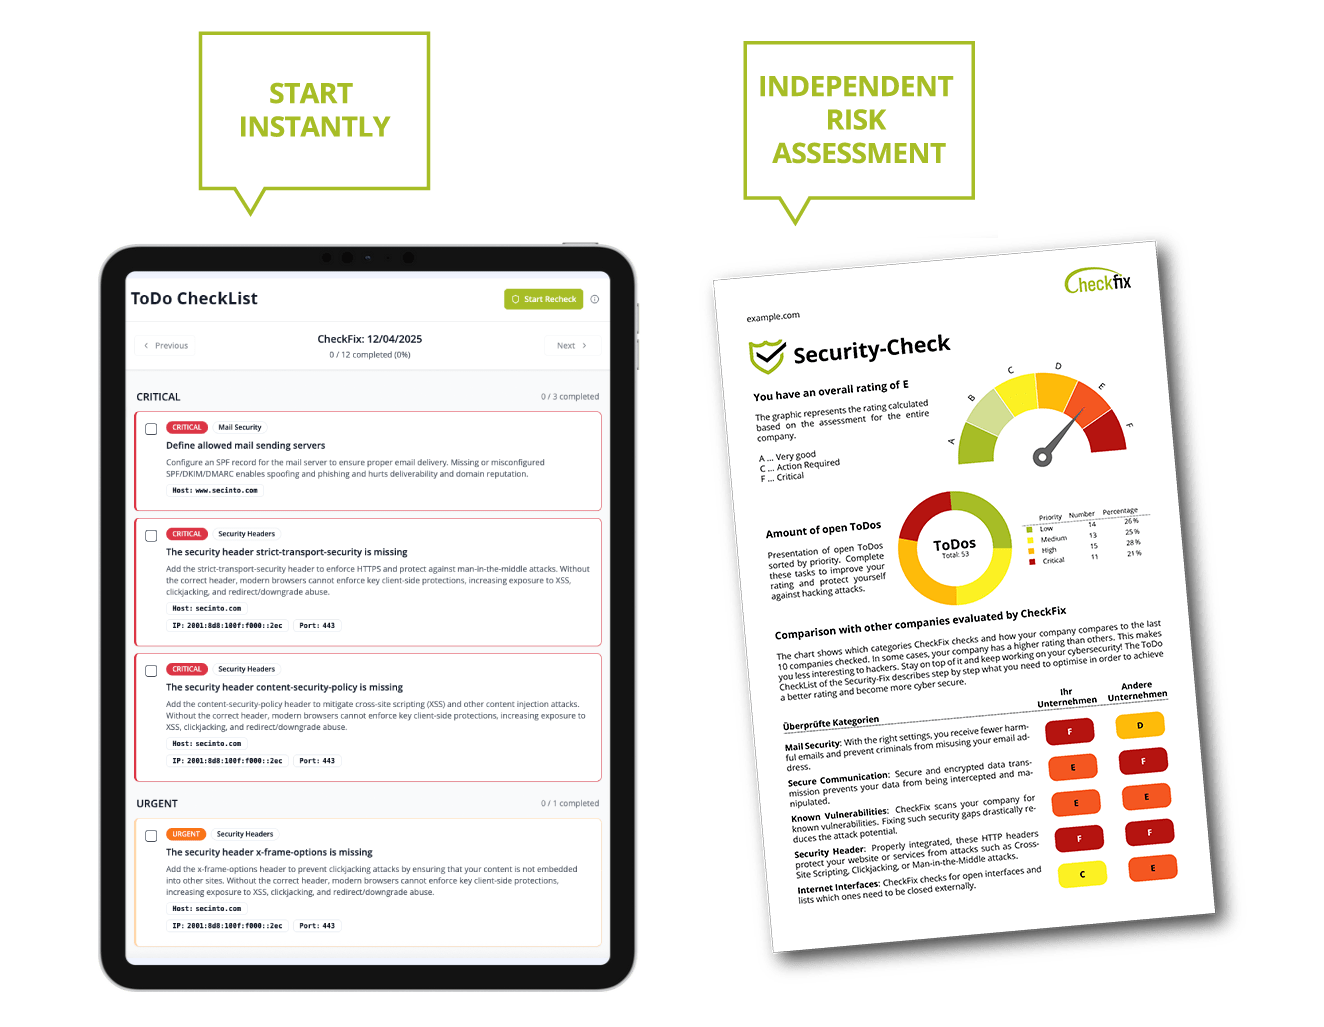
Prioritized fix strategy as a to-do list, with host and port for every finding
Dashboard Assign tasks, check off to-dos directly, track status
Markdown file for Claude or ChatGPT supports your IT during implementation
Re-check After implementation, CheckFix checks again and documents the progress
Report from the external security assessment for NIS2 and ISO 27001, plus compliance questionnaires based on DIN SPEC 27076
Many tools only show problems. CheckFix delivers the solutions – clear, actionable, verifiable.
CheckFix finds the open doors for cybercriminals – with our to-dos, you close them before attackers get in.
You request your next CheckFix and the re-check yourself, whenever you’re ready.
CheckFix, AI Pentest or traditional penetration test – which approach fits your company?
Does my company need a penetration test – AI-driven or performed by a pentester? Or is an automated tool like CheckFix enough?
All approaches have their value. What matters is where your company stands today and what goal you are pursuing.
All approaches have their value. What matters is where your company stands today and what goal you are pursuing.
CheckFix
- Passive external analysis, no intrusion
- To-do list with fix strategy, prioritized
- Regularly repeatable, re-check documents progress
- Start with a free check, predictable subscription
- Continuous improvement & proof (NIS2, ISO 27001)
- Markdown file for Claude or ChatGPT: supports your IT during implementation
AI Pentest (NEW)
- Automated penetration test by our own pentest agent on our own hardware in Austria
- Builds on the CheckFix analysis
- Freely selectable scope: individual hosts or the entire company
- Findings with all details in the dashboard, reports via the Report Builder
- 1 re-check per run, available within 4 weeks
- Run packages from € 3,900 (4 runs)
Traditional penetration test
- Active intrusion into systems by security experts
- Report with findings; implementation is up to the company
- One-time snapshot: re-check only with a new pentest
- Concrete quote including all meetings – personal support from experienced pentesters
- secinto’s pentesters (= the CheckFix developers) are available when needed
When is CheckFix the right approach?
For beginners
CheckFix is the ideal entry into cybersecurity: regular, passive external analysis with immediately actionable solutions and documented re-checks to measure success.
For companies with pentests
Companies that already run pentests use CheckFix to prepare: critical security gaps are identified early, which saves time and costs in the penetration test.
For experienced security teams
Companies that already invest in cybersecurity use CheckFix to check the effectiveness of their existing measures and the skills of their experts.
For companies that want to test more deeply
With the AI Pentest as an add-on, our own pentest agent on our own hardware actively tests the hosts you approve and shows which gaps can actually be exploited. It is also a good way to re-check changes between two manual pentests.
Conclusion for security beginners: Start with the free IT security check, close the most important gaps and document your progress. If you then want to know whether a gap can actually be exploited, add the AI Pentest as an add-on.
Pricing & Packages – What does CheckFix cost?
You can get started with CheckFix at any time. Choose one of the offers below and within 24 hours you’ll receive the FREE Security Check or the comprehensive CheckFix with to-do checklist and technical details for fixing the security gaps yourself.
FREE
Security Check
Check of your security status & risk rating
- A = Your company is highly secure
- C = Action is needed
- F = Serious security gaps
Checked in five categories:
- Mail security
- Secure communication (TLS/SSL)
- Known vulnerabilities (CVEs)
- Security headers
- Internet interfaces
Upgrade to Basic & Premium possible at any time
No hidden costs!
FREE for all new CheckFix customers
CheckFix Basic
€ 490.00 / year
2 x per year: complete external security assessment (check + re-check)
- Assessment & A–F rating overall and per category
- Same categories as the Security Check
- Complete to-do list for fixing
- Re-check after fixing = 2nd full CheckFix
- Audit-ready report with action plan
& response per finding - Dashboard with user management
- All technical details
- Assessment of up to 3 domains
- Cancel anytime
Incl. compliance questionnaires by standard: fill in and export as PDF
Recommended
CheckFix Premium
€ 950.00 / year
4 x per year: complete external security assessment
- Everything in CheckFix Basic
- Only €237.50 per CheckFix
- 4 security assessments per year
- Ongoing progress documentation
- Cancel anytime
Technical security assessment for NIS2, ISO 27001, TISAX & DORA – with documented proof for audits
Use your CheckFix as proof of security for clients and audits
Should any technical issues arise with the dashboard, we are of course on hand right away. If you need expert support, it can be booked at €150 / hour.
Specialized solutions for your company
Beyond CheckFix Basic and Premium, we offer tailored
security solutions for larger organizations and partners.
AI Pentest (NEW)
Add-on to CheckFix: active testing of your systems
- Our own pentest agent
on our own hardware - Scope: individual hosts or
the entire company - Report Builder: detailed report
per host & executive summary - 1 re-check per run included
All details on runs and packages on the AI Pentest page
CheckFix Risk Manager
For CISOs and compliance teams: assess your supply chain technically and organizationally – for NIS2, ISO 27001, TISAX® and DORA.
- Assess suppliers, subsidiaries
and subcontractors technically –
not just self-assessment - Standardized compliance questionnaires
(NIS2, ISO 27001, DIN SPEC 27076) - A–F rating and audit-ready
report per supplier - Central dashboard for
your entire supply chain
CheckFix Risk Manager: your third-party risk management with technical assessment.
CheckFix for MSPs
For IT service providers and consultants: security-as-a-service for your clients
- Multi-client dashboard
- Automated client onboarding
- Attractive partner commissions
- Branded reports for your clients
- Dedicated partner support
Offer CheckFix to your clients as an additional service
All enterprise solutions include individual onboarding, priority support
and flexible payment models. Contact us
for a tailored quote.
How good is CheckFix really?
This is what our customers say.
800+
Domains geprüft
24/7
24/7 Technical support
100%
Verified reviews
Customer experiences
FS
Franz Steinbauer
★★★★★
STEINBAUER IT GmbH, Wies
I especially like the easy-to-use interface, the appealing analysis, and the customer-focused structure. The price-performance ratio is also excellent. Thank you!
Verified review
EE
Erich Eichberger - cts GmbH
★★★★★
cts GmbH, Burgkirchen a.d Alz
We have been working with secinto for quite some time, and their product CheckFix has become indispensable for us. Due to the large number of domains we manage, we initially had no real overview of our external attack surface. CheckFix opened our eye…
Verified review
AO
Alexander Oberegger
★★★★★
CTO, smaXtec
CheckFix provides an excellent overview of the security posture of our IT landscape. We rely heavily on CheckFix to support changes in our IT and product areas from a security perspective, continuously monitor our security status, and detect vulnerab…
Verified review
SI
Sharif Ibrahim
★★★★★
eitk Elektro IT Kommunikations Gmbh, Premstätten
We used CheckFix to analyze our own domains and received a wealth of valuable insights on how to further improve our security. The report is clearly structured and highlights details you wouldn’t normally think of. We highly recommend CheckFix to any…
Verified review
SS
Simon Schmelzer-Ziringer
★★★★★
EDV & IT Schmelzer-Ziringer, Trahütten
The software detects even the smallest security gaps that other tools often miss. Particularly impressive is the high speed of its analyses — without compromising accuracy. In addition, it’s extremely easy to use, allowing even less experienced users…
Verified review
How can cyberattacks hit your company?
Real-world examples of hacking attacks
AI attacks the same way, but finds gaps faster. With the AI Pentest you test your systems with the same tools before someone else does.
If attacks can look like this – how secure is your company really?
Check your external attack surface for free – clearly, quickly and from a hacker’s perspective.
Security check from the outside
from a hacker’s perspective, without penetrating the system
Clear overview through ratings
see immediately where action is needed
To-do list
concrete measures to work through
Re-check with report
usable for customers, auditors or internal documentation
Frequently asked questions
How do I check the security of my website?
The security of your website isn’t decided by the website alone. Anything reachable from the outside can be attacked: web servers, mail servers, open ports, SSL/TLS encryption and DNS. CheckFix checks this entire external attack surface in one run, shows a grade from A to F for each area and delivers a prioritized to-do list for your technician to work through.
How do I find vulnerabilities in my IT infrastructure?
There are two ways to find security gaps: manual security audits or penetration tests – or automated tools that check your IT systematically and regularly for known vulnerabilities.
Proven methods for finding vulnerabilities:
- External assessment from a hacker’s perspective (open ports, SSL/TLS, DNS, email security)
- Matching your software versions against CVE databases for known security gaps
- Checking the configuration of web servers and mail servers
- Identifying outdated or forgotten systems (shadow IT)
The key difference is between the internal and the external perspective: internal audits check your systems from the inside – an external attack surface analysis shows exactly what attackers would see from the outside, meaning the doors hackers actually use to get in. More than 70% of all cyberattacks start from the outside, which is why the external view matters so much.
CheckFix handles this external search for vulnerabilities fully automatically: within 24 hours you receive a complete overview of all security gaps found – including a prioritized to-do list with a concrete fix strategy that your own technician can implement.
What does CheckFix check?
CheckFix analyzes your entire external attack surface: domains, subdomains, email servers, open ports, SSL certificates, DNS configuration, web technologies and mail security (SPF, DKIM, DMARC).
Specifically, CheckFix checks:
- Your email addresses for misconfigurations
- Known vulnerabilities (CVEs) in identifiable technologies
- Open ports and outdated SSL/TLS protocols
- Missing or misconfigured security headers on your websites
- DNS and mail security settings
Everything that can be reached from the outside via your domain(s) is checked – just as hackers would use automated tools.
Important: CheckFix does not replace virus protection; it adds an external perspective to your existing security measures. No tool can detect zero-day vulnerabilities (unknown security gaps) – CheckFix finds known vulnerabilities (n-day) before attackers exploit them.
Who is CheckFix suitable for?
CheckFix is suitable for any company with an online presence: website, email server or publicly accessible APIs. SMEs benefit in particular (professional IT security without five-figure pentest budgets), as do companies subject to NIS2 (technical compliance support and supplier assessment), suppliers to companies subject to NIS2 or ISO 27001 (proof of security for customers) and IT service providers/MSPs (customer assessment and inventory monitoring).
What is the difference between CheckFix and a penetration test?
A penetration test actively attacks your systems and shows which gaps can actually be exploited. CheckFix, on the other hand, analyzes your external attack surface from the outside without penetrating your systems, and delivers a prioritized fix strategy. You can do this regularly at a predictable subscription price. A manual penetration test of comparable scope can easily cost 15,000 euros. We offer active testing as an add-on: the AI Pentest.
What is the difference between CheckFix and the AI Pentest?
CheckFix analyzes your external attack surface passively and delivers a prioritized to-do list with a fix strategy. The AI Pentest builds on this: our own pentest agent on our own hardware actively tests the hosts you approve and shows which gaps can actually be exploited. You book it as an add-on to your CheckFix, in packages starting at 4 runs.
Can my technician fix the security gaps themselves?
Yes! That’s exactly what CheckFix was built for. Every vulnerability is translated into to-dos with a fix strategy – clear to any competent technician. You do need one, though, because it’s impossible to provide a concrete step-by-step guide for every system. Whoever set up your IT can now fix the security gaps too. On top of that, a pre-prompted Markdown file that you can feed into ChatGPT, Claude and co. helps with the implementation in your specific environment (Plesk, cPanel, Azure, AWS etc.). A system administrator is no substitute for a cybersecurity expert – but CheckFix translates security know-how so that your technician can implement it without five-figure consulting costs.
What is the difference between CheckFix and virus protection?
Virus protection (antivirus) protects your devices against malware from the inside. CheckFix analyzes your company from the outside – like a hacker. The two approaches complement each other: antivirus fends off attacks that are already in the system. CheckFix prevents attackers from getting in at all by finding open doors (ports, misconfigurations, outdated software) before you get hacked. Best option: use both!
How often should I run CheckFix?
At least twice a year. Why? New vulnerabilities appear all the time (software updates, new subdomains, configuration changes). After each check, your team needs time to fix things – the re-check shows measurable progress. Semi-annual checks match common compliance cycles (ISO 27001, NIS2) and keep you secure between pentests. This turns security into a routine rather than a chore.
Can I use the report as proof for audits (NIS2, ISO 27001, TISAX)?
Yes. You document open items directly in the to-do list with reason, compensating measure, deadline and owner. This produces a PDF report with an action plan and management response that you can pass on to customers or use for internal audits and documentation under NIS2, ISO 27001 or TISAX®. The report covers the technical part of the external security assessment.
Do I need a penetration test for NIS2 or NISG 2026?
The NISG 2026 does not explicitly require a penetration test. It does, however, require policies and procedures to assess the effectiveness of your risk management measures, and a structured approach to handling vulnerabilities. Essential entities, such as operators of critical infrastructure in energy, health or transport, must also expect audits by an independent body. A penetration test is a common technical proof for this.
Whether you need one depends on your classification and your risk analysis. With CheckFix you know your external attack surface; with the AI Pentest you check what can be exploited.
800+
domains checked
70%
of all cyberattacks
start from the outside
start from the outside
85%
find critical vulnerabilities
Start now
Protect your company before it’s too late
Start your free IT security check now
100% free
No credit card required
Results in 24h
No credit card required
Results in 24h